Framework language is preserved
Reports use the concepts and status language of the selected framework rather than forcing every view into Core risk terminology.
Framework-specific assessment
Aegis101 combines a stable risk-assessment foundation with governed framework views that retain each framework's structure, terminology, uncertainty, and limitations.
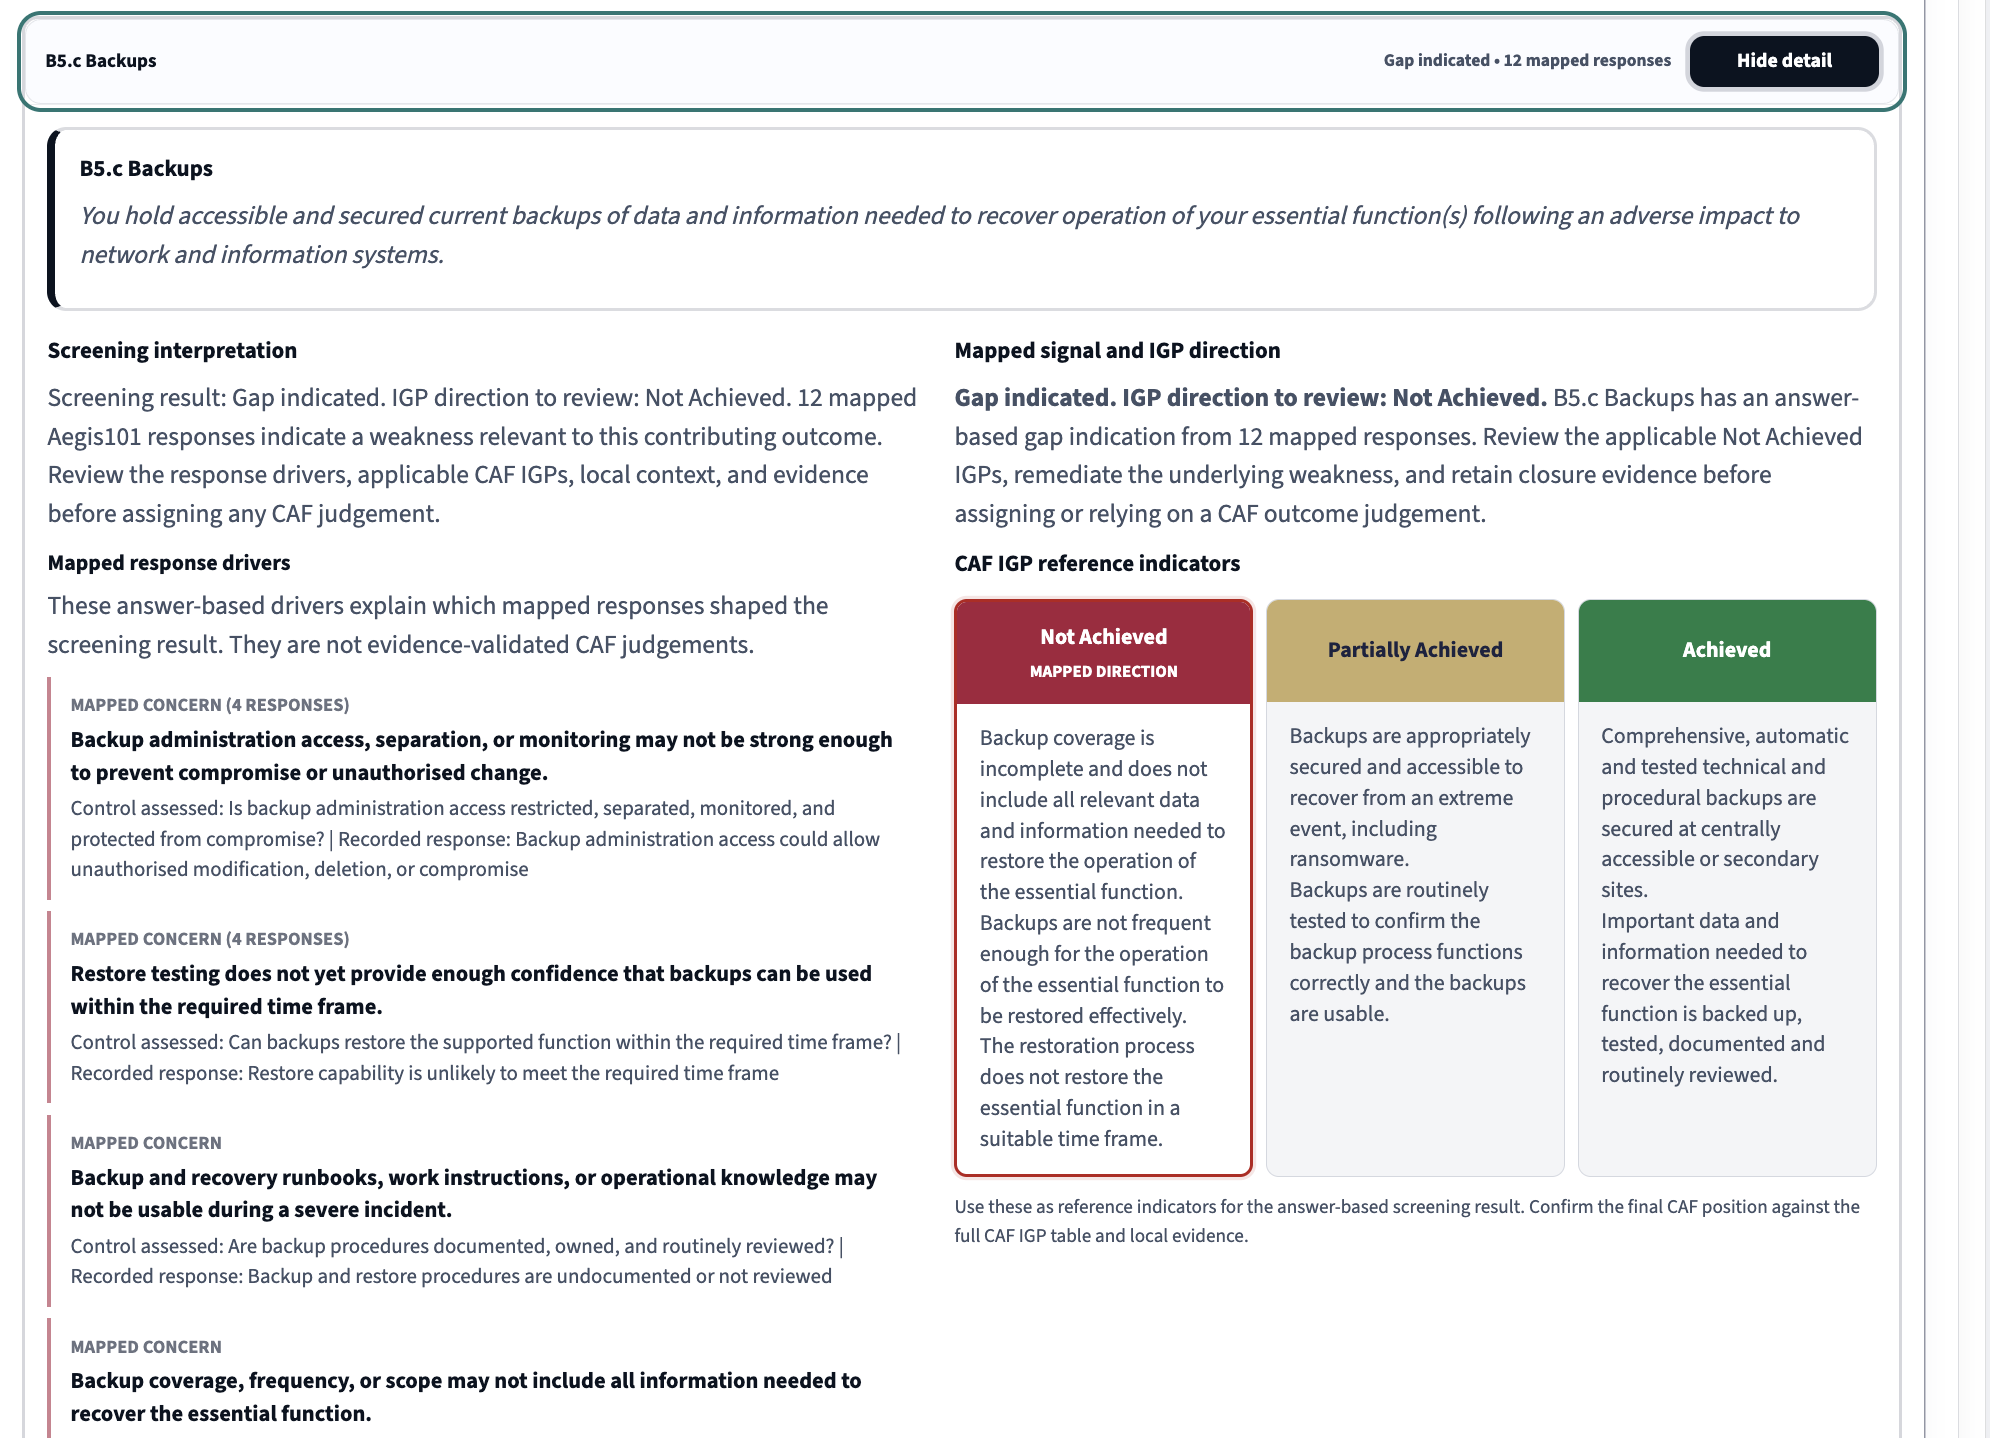
The CAF view is answer-based mapped screening. It supports review and prioritisation; it is not a formal CAF assessment or evidence-validated judgement.
A governed portfolio
Each view shows how the submitted answer basis connects to the framework, where information remains incomplete, and what requires further evidence or judgement.
Core assessment captures context, routes questions, interprets submitted answers, identifies material weaknesses, and directs remediation and evidence follow-up.
Each framework is introduced through controlled mapping, framework-specific language, routing, report treatment, and explicit assurance boundaries. The portfolio can grow without making one framework the identity of Aegis101.
Governance principles
Adding breadth must not weaken the integrity of the interpretation.
Reports use the concepts and status language of the selected framework rather than forcing every view into Core risk terminology.
Users can understand which answer basis contributed to a framework view and where further judgement or evidence is needed.
Unresolved mapped controls remain Not Assessed or insufficient basis. Missing information cannot create a favourable framework direction.
An answer-based indication does not become an audit finding, compliance decision, certification, or evidence-validated outcome.
First framework implementation
The CAF view organises mapped response signals against CAF objectives, principles, contributing outcomes and applicable Indicators of Good Practice direction. It is not a formal CAF assessment.
Growing coverage
Recognised security, resilience, and technology standards are introduced through governed views that retain their structure, interpretation, outstanding states, and compatible assessment history.
Register interest to discuss current framework-specific reporting and the standards that would provide the greatest practical value to your organisation.